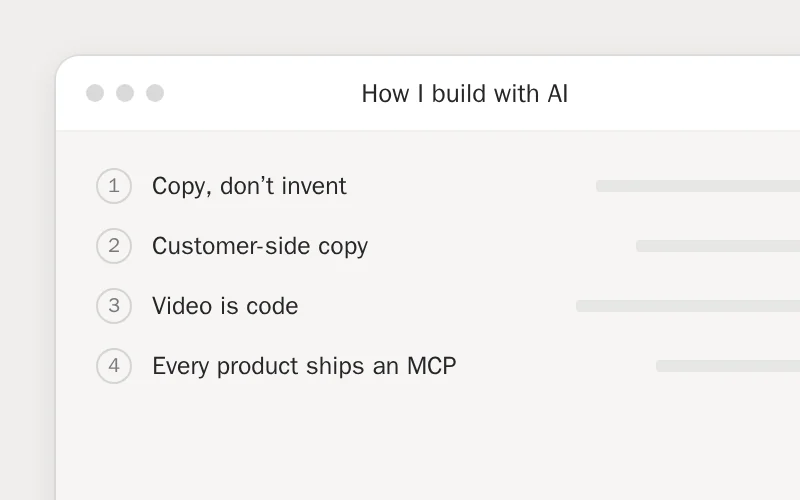
- MCP server from day one, mapped to the same core functions as the UI. Stateless streamable HTTP, auth per request.
- Agents get their own tokens, shown once and stored hashed, with per-tool
allow / ask / deny.askbecomes an approval I tap. - Outsiders get a scoped proxy, not my keys. For example, a colleague gets one Postiz channel through my MCP hub: one URL per person, only the allowed tools, every call logged, revocable.
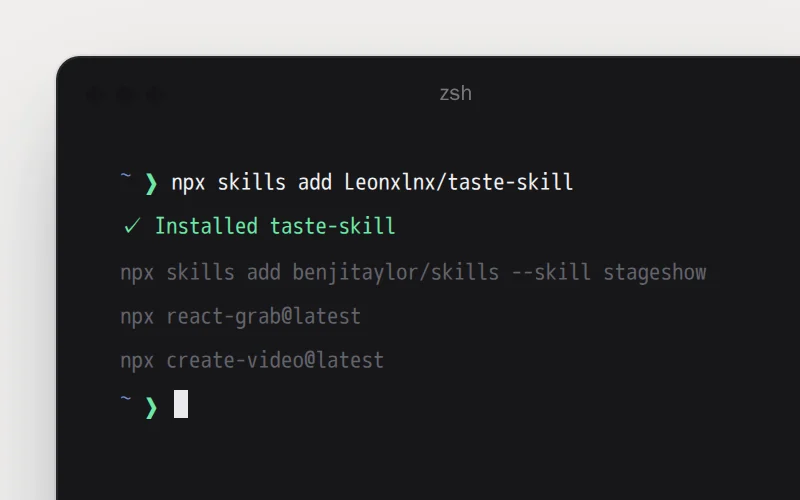
claude mcp add --transport http <name> https://mcp.example.com/<slug> \
  --header "Authorization: Bearer <token>"